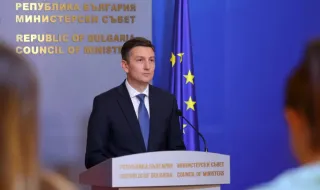
Hackers had covert access to the networks of the Bulgarian state administration for five years and exfiltrated at least 130 gigabytes of government documents. This was announced by Minister Ivan Vasilev, who described the incident as the longest-running and most extensive known cyberespionage campaign against the Bulgarian administration.
The attack began in 2021. The hackers gained access to systems used by institutions to exchange documents, moved between separate components of the infrastructure, and collected sensitive information about the work of the state.
“The investigations so far have found no compromise of the personal data of Bulgarian citizens,” Ivan Vasilev stressed.The Breach Was Discovered in August
The unauthorized access was detected in August through the new national cybersecurity system, which enables centralized monitoring of government networks. According to Vasilev, the attack went undetected for years because until then the security tools had operated separately.
Following the discovery of the breach, an interagency group was formed with experts from the Ministry of Innovation and Digital Transformation, the Ministry of Defence, the Cybercrime Directorate of the Directorate General for Combating Organized Crime, the State Agency for National Security, the State Intelligence Agency, the Military Intelligence Service, and the Executive Agency for Electronic Governance Infrastructure.
Information Services AD, representatives of the private sector, and international partners, including the European Union Agency for Cybersecurity, also took part in the operation.
Affected Networks Remain Under Surveillance
During the first phase, the scope of the breach was established, after which the affected environment was isolated and access controls for critical systems were tightened. The channels through which the hackers had maintained their presence on the networks were cut off.
All cases of unauthorized access identified so far have been terminated. The teams continue to address the vulnerabilities and introduce stricter access rules.
The affected infrastructure will remain under enhanced monitoring for 90 days. The aim is to identify any potential new intrusion attempts in a timely manner.
Sources: novini.bg